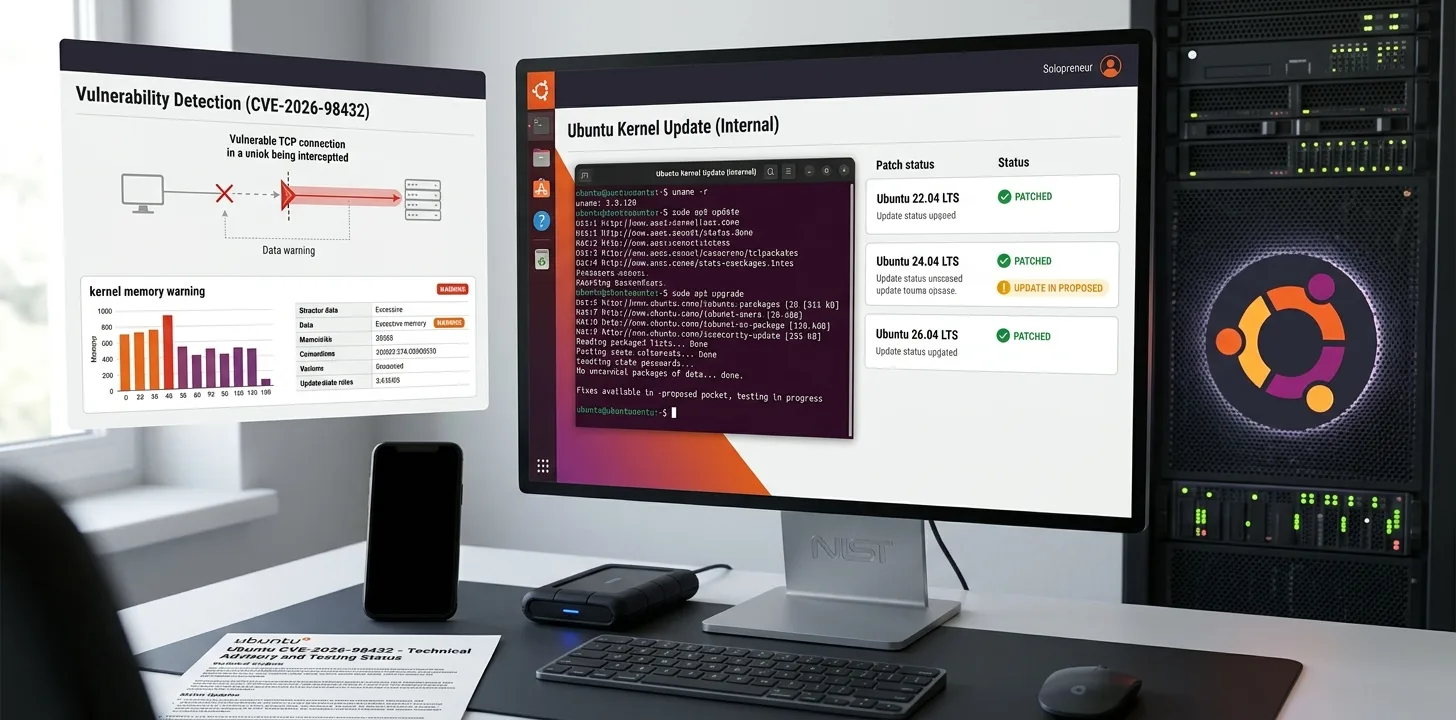
The Ubuntu kernel vulnerability CVE-2026-98432 is a remote flaw in the Linux kernel's IPv4 TCP handshake code. Ubuntu rates it 9.8 (Critical) with High priority. As of its security page, last updated October 30, every supported Ubuntu release from 16.04 to 26.10 is still listed as vulnerable. Fixes are "work in progress" for 22.04, 24.04, 26.04 and 26.10.
What CVE-2026-98432 is
When a TCP handshake completes, the kernel hands the pending connection's IP options to the new socket without copying them. A retransmitted SYN handled on another CPU can then read memory that has already been freed. This is a use-after-free.
- It can be triggered remotely, with no login.
- It affects kernels from Linux 4.4 onward.
- A second path exists when
net.ipv4.tcp_migrate_req=1or a BPF reuseport migration program is in use. - IPv6 is not affected by the main race.
Which Linux distributions are patched
This table combines Ubuntu's page with vendor statuses collected by Cyber Kendra as of October 29. Check your vendor's page for the latest status.
| Distribution | Status |
|---|---|
| Ubuntu 22.04, 24.04, 26.04 LTS and 26.10 | Vulnerable, fix in progress |
| Ubuntu 16.04, 18.04, 20.04 | Vulnerable |
| Ubuntu 14.04 | Not affected |
| Debian 12 and 13 | Fixed |
| Oracle Linux 7 to 10 (UEK) | Fixed |
| openSUSE Leap 16.0 | Fixed |
| Amazon Linux 2023 (kernel 6.12 and 6.18) | Fixed |
| RHEL 8, 9 and 10 | Listed as vulnerable on Oct 29. Check Red Hat's page for updates. |
| RHEL 7 | Not affected |
Fixed upstream stable kernels include 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113 and 6.18.56.
How to check your Ubuntu server for the kernel vulnerability
- Run
uname -rto see the kernel you are actually running. - Compare it with the fixed version on Ubuntu's CVE page once one is published.
- Run
sudo apt update && sudo apt upgradewhen the fix lands. - Reboot. A new kernel does nothing until the machine runs it.
- Run
sysctl net.ipv4.tcp_migrate_req. A value of 1 means the second path applies to you.
What to do while Ubuntu has no fix
- Limit which servers expose TCP services to the internet.
- Put public services behind a firewall or load balancer you control.
- Turn on unattended security upgrades so the fix installs as soon as it ships.
- Plan a reboot window now, so you can patch quickly.
Red Hat says no available mitigation meets its standards, so a patched kernel is the only real fix.
Is it being exploited?
No vendor advisory reports attacks, and the flaw is not in CISA's Known Exploited Vulnerabilities catalogue, per Cyber Kendra. Anthropic has said its internal research model built a working remote root exploit for servers with a multipath TCP listener. It has not released the code.
Frequently Asked Questions
Do I need to reboot after patching?
Yes. Installing a fixed kernel does not protect you until the machine is running it. Check with uname -r after the reboot.
Which kernel versions fix CVE-2026-98432?
Upstream stable releases 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113 and 6.18.56 include the fix. Distribution kernels use their own version numbers, so check your vendor's advisory.
Is Ubuntu patched for CVE-2026-98432?
Not yet. Ubuntu lists all supported releases as vulnerable, with fixes in progress for 22.04 and newer.
How serious is CVE-2026-98432?
Ubuntu and the kernel CVE team score it 9.8 out of 10. Red Hat rates it 8.1.
Is IPv6 affected?
Not by the main race. Ubuntu says IPv6's migration issue will be fixed in a separate patch.
Summary
CVE-2026-98432 is a critical remote TCP flaw in Linux kernels from 4.4 onward. Debian, Oracle Linux and others have shipped fixes, but Ubuntu kernels are still listed as vulnerable. Watch Ubuntu's page, patch the moment a fix ships, and reboot.
Related articles
Sources
We cover gaming, software, tech, AI and trading. Every story links to its primary sources, and rumours are labelled as such. Spotted a mistake? Let us know and we will correct it.
Comments
Loading comments…